Category: All
Supabase Row Level Security: Fix Data Leaks in Lovable Apps
Supabase Row Level Security for Lovable apps: how tables end up exposed to the anon key, how to test yours in ten minutes, and policies that fix it.
Samrat
AI-Built App Production Readiness: A Founder's Launch Checklist
AI-built app production readiness explained: what to fix in a Lovable or Bolt app before real users and payments arrive, with a clear launch checklist.
Samrat
Authentication for SaaS Startups: A Founder's Guide to Auth, SSO, and API Security in 2026
Every SaaS product runs on one invisible layer that decides who gets in and what they can touch: authentication and authorization. Get these wrong and you inherit account-takeover risk, tenant data leaks, and a security review that can stall an enterprise deal or a funding round. This founder-friendly guide breaks down sessions, JWTs, OAuth, and SSO in plain terms, shows you how to design role-based access control for a multi-tenant product, and gives you a practical roadmap for hardening auth as you grow from first user to first enterprise contract.
Samrat
When Not to Use Django (And What to Use Instead)
Django is widely recognized for its “batteries-included” philosophy, enabling rapid web application development with features like authentication, ORM, admin interface, and more out of the box. It’s a fantastic choice for monolithic web apps, content-heavy platforms, and admin dashboards.
Samrat
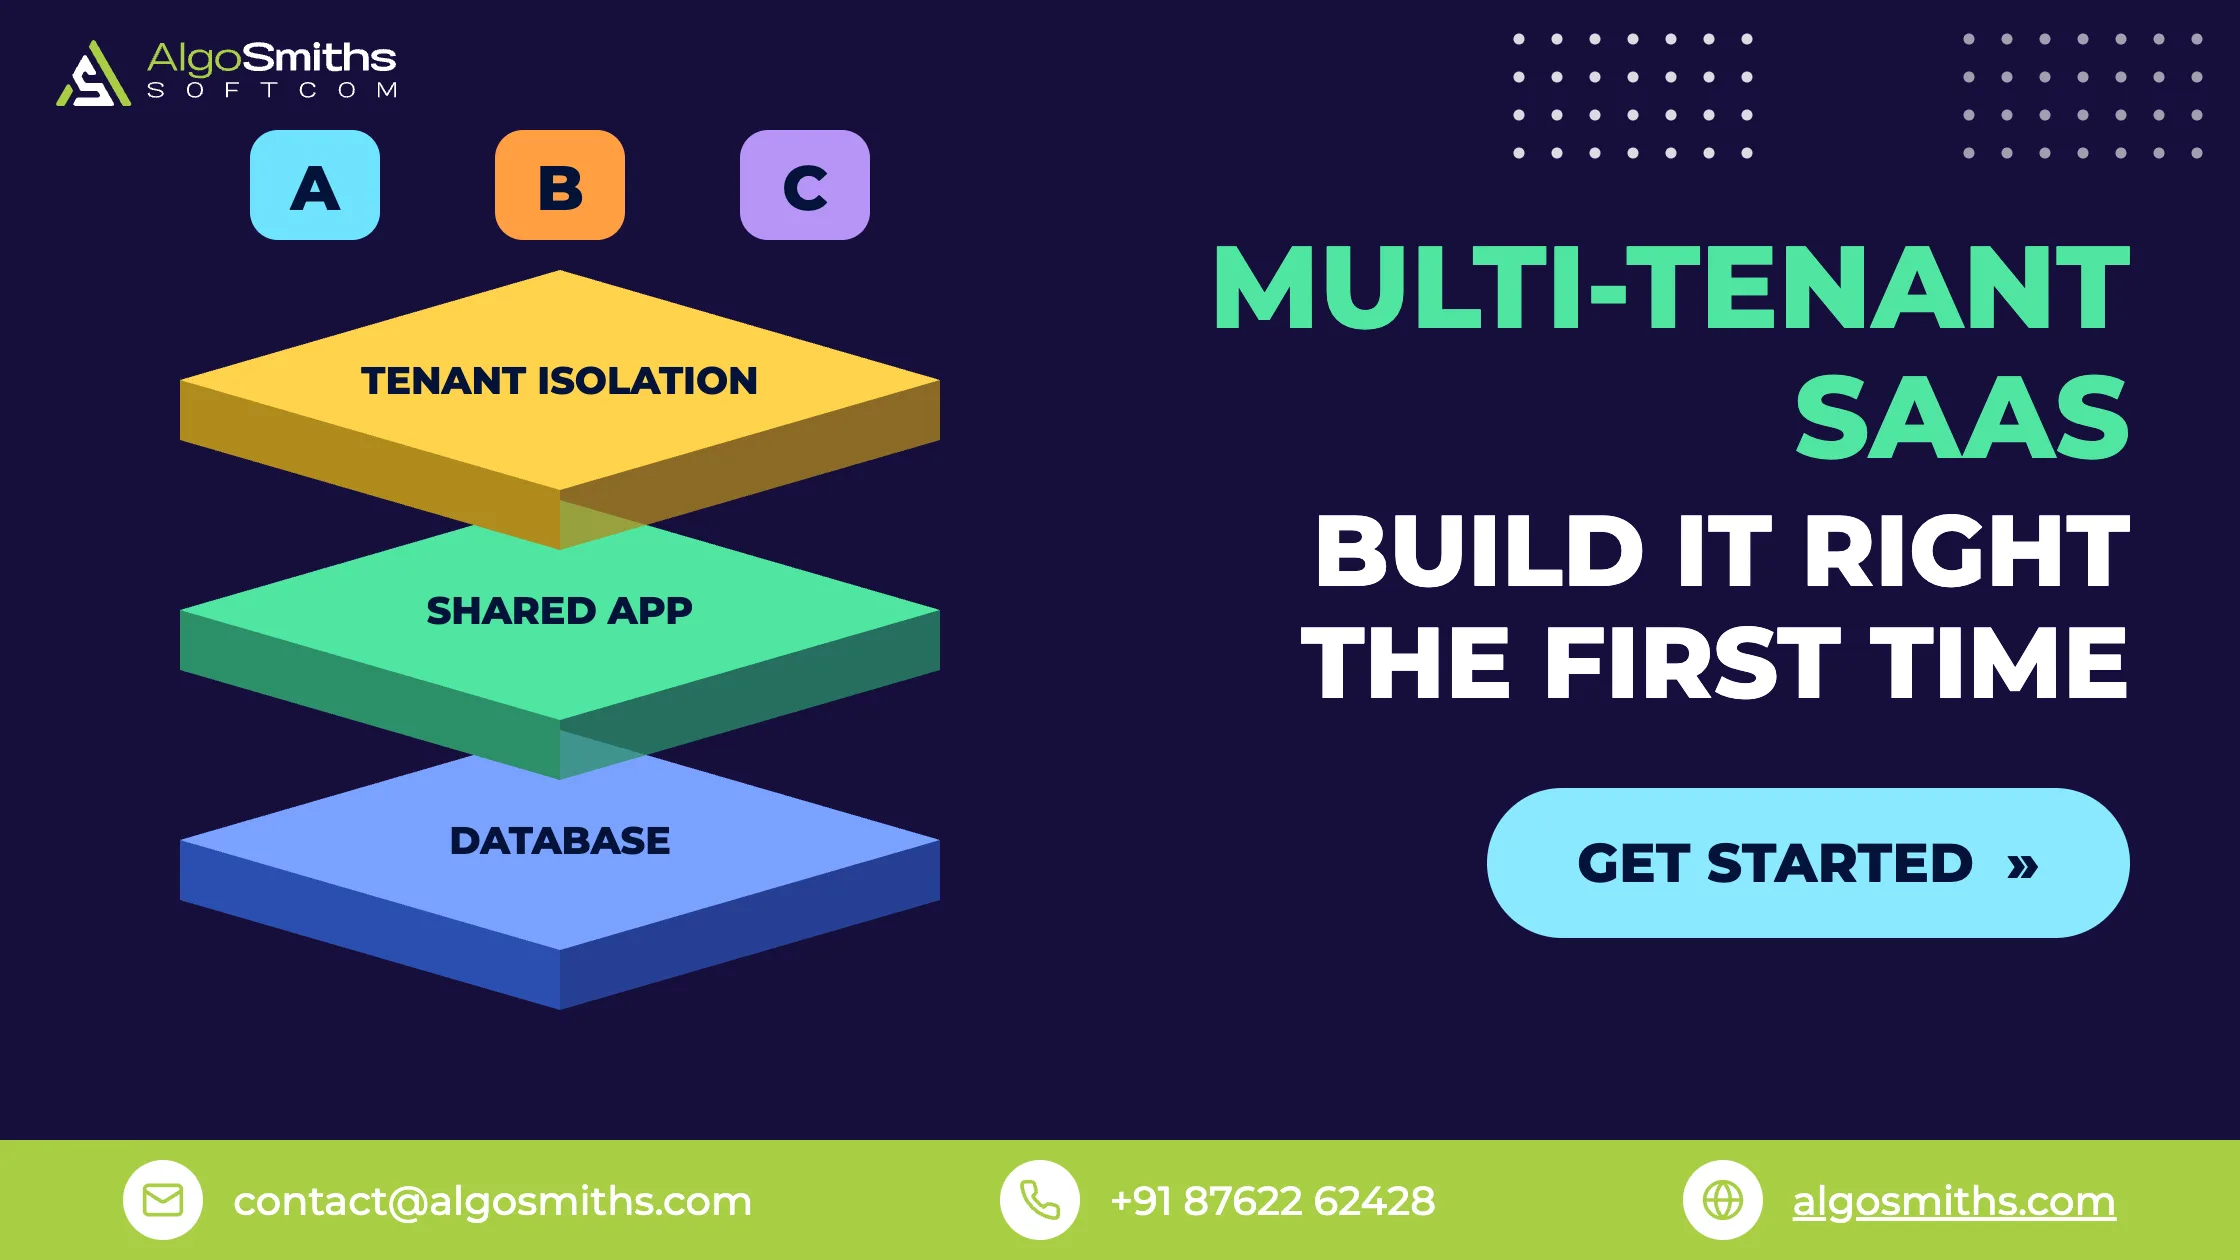
Multi-Tenant SaaS Architecture: A Founder's Guide to Building It Right the First Time
Building a multi-tenant SaaS product means locking in foundational architecture decisions before you write your first line of code. This guide breaks down the three core multi-tenancy models, shows you how to choose between shared and isolated databases, and highlights the security and scaling mistakes that force a costly rewrite later. Whether you're scoping your first B2B MVP or preparing to onboard your first enterprise customer, this is the practical framework to get your architecture right the first time.